API security, traffic management and monitoring in one platform
apiRuler is a central layer between your clients and your services. From one visual console it applies every policy, from authentication to circuit breaking, to each route with the same standard.
Over your API traffic, full control and visibility
Bring scattered configurations into one place. Apply security, routing and monitoring policies to every service with the same standard.
APIs keep multiplying, managing them gets harder
Every new service arrives with its own rules. Soon nobody can say for sure how each API is protected, where the traffic goes or what is causing the slowdown.
In modern systems the hard part is not building APIs. It is managing them sustainably.
Clients
 apiRuler
Backend Services
All traffic passes through one point and is managed from one place
apiRuler sits between your clients and backend services. Authentication, routing, security, traffic management and monitoring run in the same layer on every request, with no changes to your service code.
- Host, path and method based routes
- Ready integrations with Grafana, Prometheus, ELK, Keycloak and Redis
- On-Premise, Kubernetes and Cloud / Hybrid installs
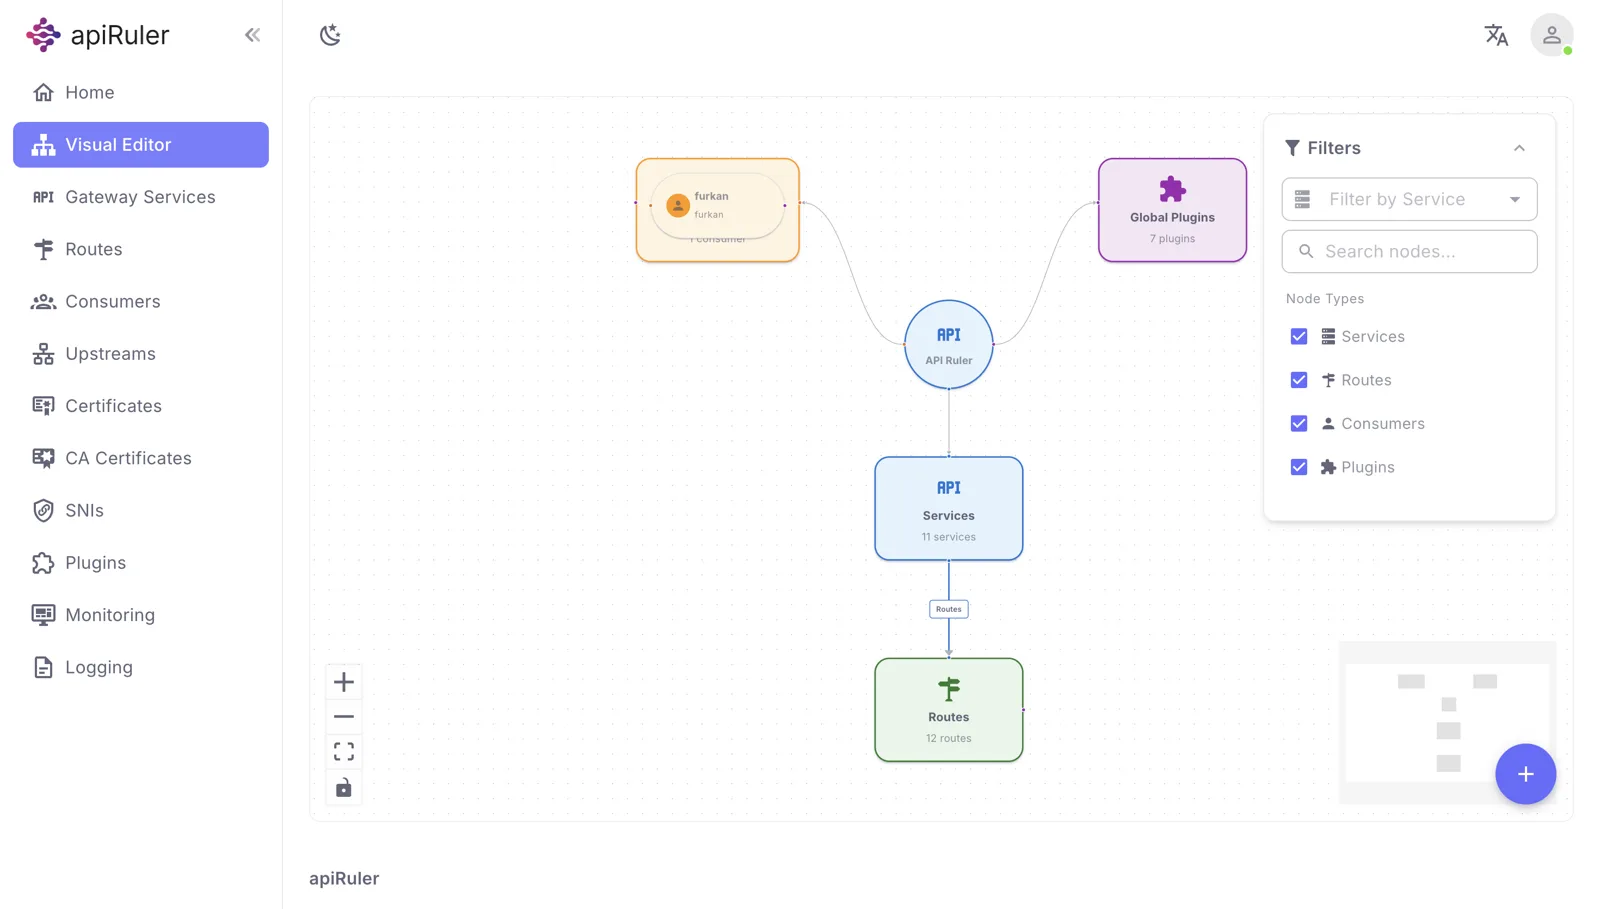
One Console
- Route
- Service
- Consumer
- Certificate
- Load Balance
- Plugin
- Monitoring
Manage every component from one console and stay in control
Define routes, services, consumers, certificates, load balancing and plugins from the web UI. Design traffic flows with drag and drop in the visual editor instead of editing config files.
Import Cloudflare configurations and track SNIs and CA certificates in one place.
Explore the consoleAuthentication
Authentication
- JWT
- OAuth2
- API Key
- LDAP
- HMAC
- Session
Authorization
Authorization
- IP Restriction
- CORS
- SSL / TLS
- Bot Detection
- Rate Limit
- ACL
Protection at every layer, confidence in every scenario
Protect your APIs at every level with a layered security approach. Define authentication and authorization policies per service or per consumer, and renew certificates automatically with Let's Encrypt.
- Connects to your corporate identity stack through Keycloak and LDAP
- Rate limiting per service and per consumer
- A complementary layer behind your existing WAF
GatewayManage all incoming traffic intelligently
apiRuler protects your resources and improves performance. Apply policies such as load balancing, caching and circuit breaking to each route separately.
Hover over a policy to see what it does.
Take a closer look
Central management instead of scattered configs. Real apiRuler screens.
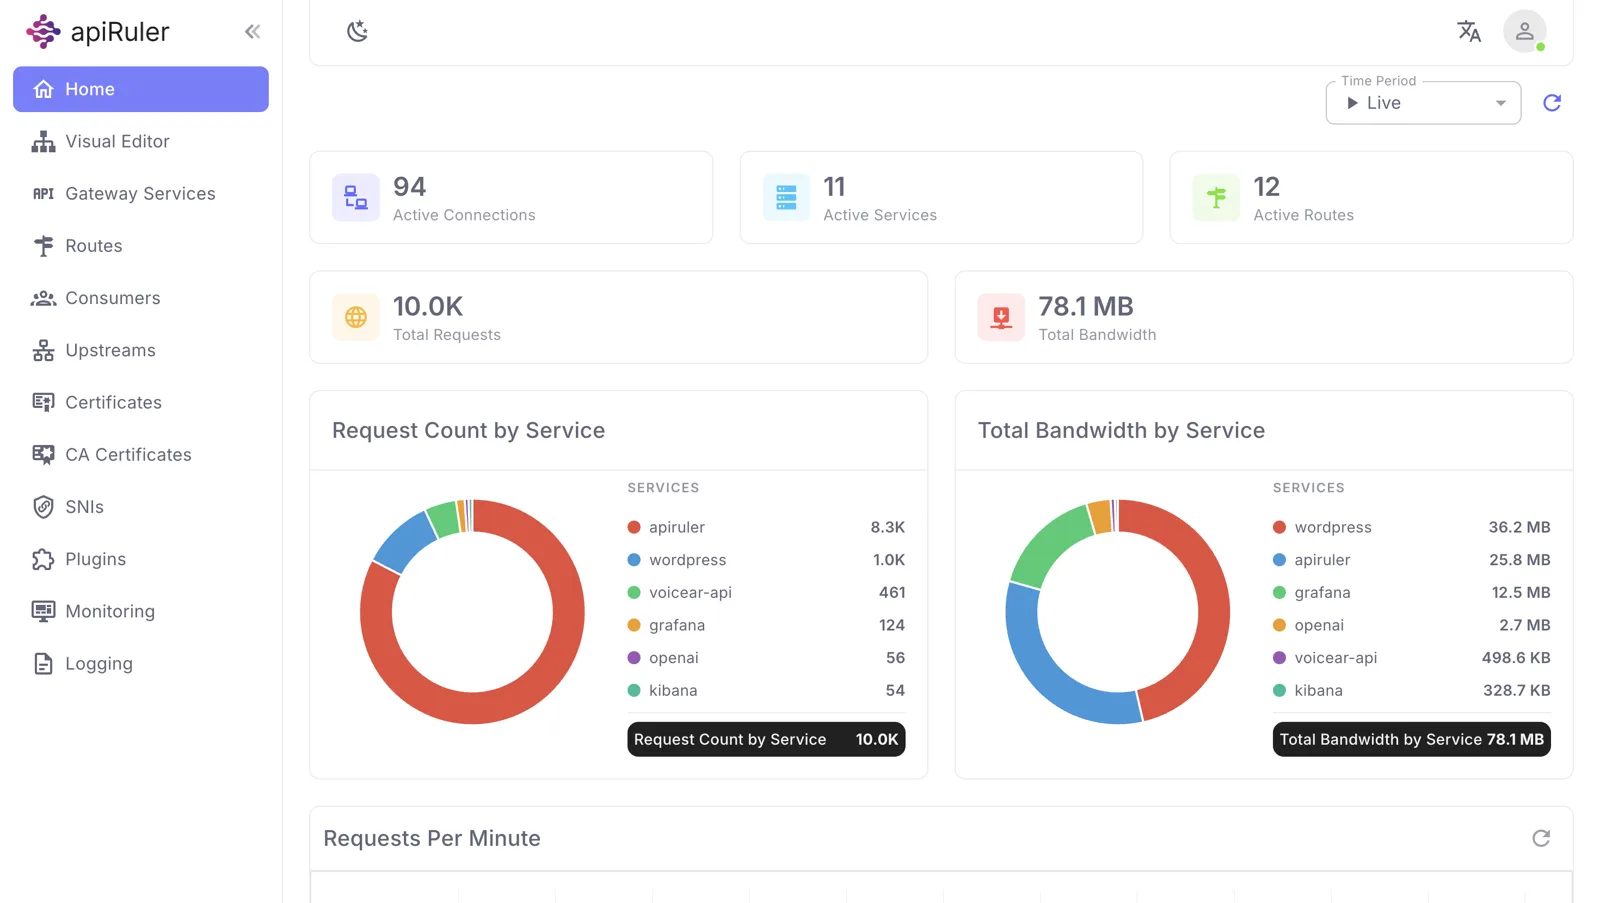
Home: active connections, services, routes and request / bandwidth breakdown per service.
What does apiRuler bring your organization?
Less operational load
Central management instead of configuring APIs one by one.
Stronger security
Identity, authorization, traffic and policy controls in one place.
More visibility
API traffic, logs and metrics monitored centrally.
Faster integration
New services join your existing architecture with less effort.
Ready to take control of your APIs?
Our team is ready to plan the right deployment for your infrastructure with you and show you a live demo.